
pqdoctor
A single-file command-line tool for Windows, macOS and Linux. Check one server, scan thousands, check mail over STARTTLS or SSH. JSON output and exit codes for CI.
pqdoctor
A single-file command-line tool for Windows, macOS and Linux. Check one server, scan thousands, check mail over STARTTLS or SSH. JSON output and exit codes for CI.
Flarebox
A desktop app for Cloudflare, for Windows and Linux. Local Workers projects, deploys, your zones through the API, and pqdoctor on every origin with history, fix reports and a CBOM.
✘ github.com:443 (140.82.114.4)  Not post-quantum  TLS 1.3 works, but when offered X25519MLKEM768 the server asks for X25519 instead. Its TLS library doesn't have ML-KEM, or the groups are limited in config.  cause: no-mlkem
Fixes 1. Upgrade the TLS library under the server Hybrid PQ (X25519MLKEM768) ships in OpenSSL 3.5+, current BoringSSL and AWS-LC, Go 1.24+ and rustls with aws-lc-rs. If curves are set by hand, add X25519MLKEM768 to the front of the list. # Go cfg.CurvePreferences = nil // Go 1.24+ default includes X25519MLKEM768 # OpenSSL-based Groups = X25519MLKEM768:X25519:prime256v1 2. Can't upgrade? Cloudflare Tunnel Run cloudflared next to the server. The tunnel from the server to Cloudflare already uses post-quantum key agreement, so the hop that leaves your network is protected even if the server isn't. cloudflared tunnel run <tunnel-name>✘ nginx.org:443 (3.147.99.198) Not post-quantum: TLS 1.2 only The server doesn't speak TLS 1.3, so it can't do hybrid ML-KEM. cause: tls12-only server: nginx/1.31.3
Fixes 1. Turn on TLS 1.3 # nginx ssl_protocols TLSv1.2 TLSv1.3; 2. nginx: link against OpenSSL 3.5+ and list the PQ group ssl_protocols TLSv1.2 TLSv1.3; ssl_ecdh_curve X25519MLKEM768:X25519:prime256v1;✔ cloudflare.com:443 (104.16.133.229) Post-quantum: negotiates X25519MLKEM768 Supports and prefers hybrid ML-KEM key exchange. cause: pq-preferred server: cloudflare✔ ssh github.com:22 (140.82.114.4) Post-quantum: offers mlkem768x25519-sha256, sntrup761x25519-sha512, sntrup761x25519-sha512@openssh.com The server offers a hybrid post-quantum key exchange. A client that also has one (OpenSSH 9.0+) uses it. server: 1f08b963 strict kex: yes ! Not CNSA 2.0: that needs ML-KEM-1024 (mlkem1024nistp384-sha384). X25519 and P-256 hybrids are fine for everyone else.Seven handshake-only probes tell the causes apart: an old TLS library, a hand-written curve list, TLS 1.2 only, the pre-standard Kyber draft, or a middlebox that drops large ClientHellos. How it works.
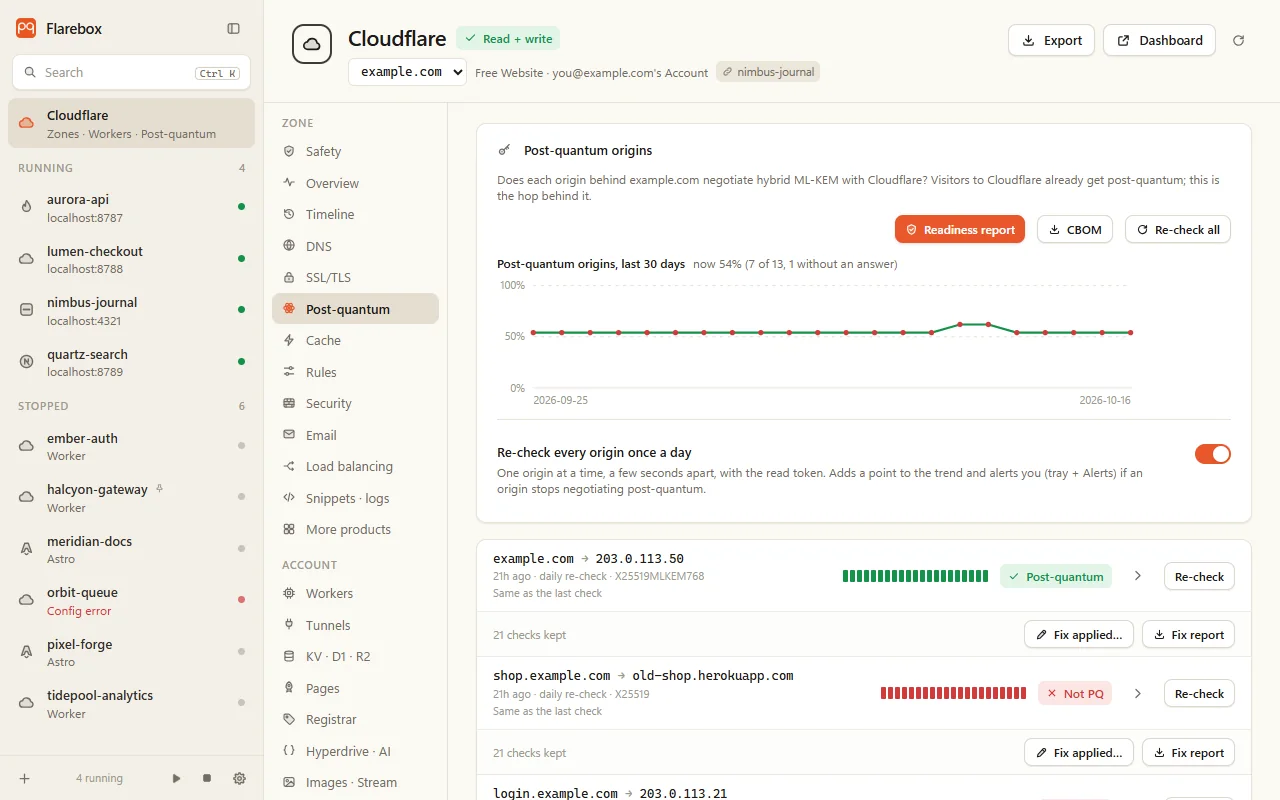
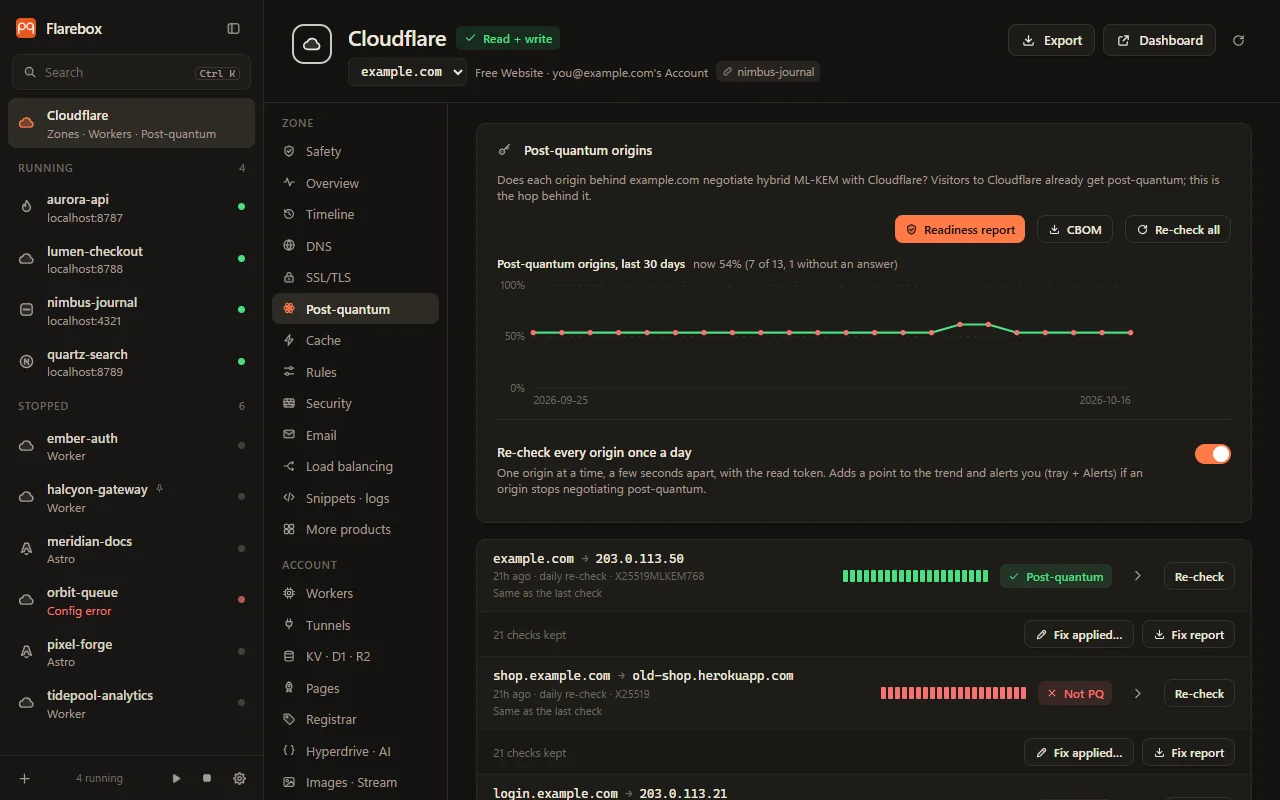
Flarebox checks every origin behind your proxied DNS records, re-checks them daily, alerts on regressions, and turns a fix into a before/after report and a CycloneDX 1.6 CBOM. Post-quantum tab.
pqdoctor and Flarebox are MIT-licensed, independent projects by Kalyan Gopalam. Not affiliated with or endorsed by Cloudflare.